
Security
Twitter Under Siege: Fake Apple Pay/Zelle Scams, 12+ Hour Recovery, and the 2FA Debate
High-profile Twitter accounts are being hijacked and used to push fake Apple Pay/Zelle laptop scams while recovery can take 12+ hours. Users urge @elonmusk to clarify 2FA access, speed up support, and harden defenses.
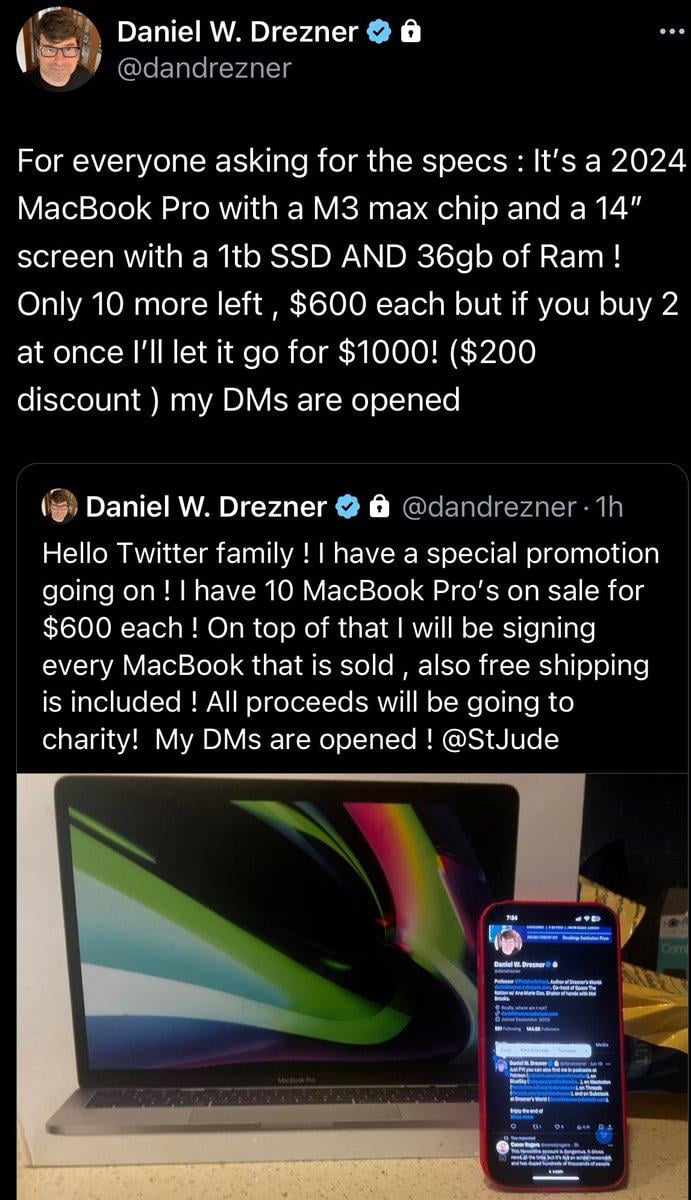
Over the past weeks I've been seeing a pattern: high-profile Twitter accounts are being compromised, and the attackers immediately try to convert the breach into quick cash by offering fake laptop deals and asking buyers to pay via Apple Pay or Zelle. Because Twitter's support is limited, account owners can be locked out for 12+ hours – a lifetime for real-time scams. That delay amplifies the damage; followers trust verified accounts, the scams spread fast, and victims lose money. The thread calls on @elonmusk: what can be done to reduce the window of attack and speed up recovery?
When big accounts are hijacked: fake laptop deals and fast money grabs
Over the past weeks I've been seeing a pattern: high-profile Twitter accounts are being compromised, and the attackers immediately try to convert the breach into quick cash by offering fake laptop deals and asking buyers to pay via Apple Pay or Zelle. Because Twitter's support is limited, account owners can be locked out for 12+ hours – a lifetime for real-time scams. That delay amplifies the damage; followers trust verified accounts, the scams spread fast, and victims lose money. The thread calls on @elonmusk: what can be done to reduce the window of attack and speed up recovery?
Influx of malicious accounts: is Twitter leadership doing enough?
Some tweeters framed this as an invasion: 'hackers are pouring into Twitter like illegal migrants into a country' – a blunt metaphor aimed at leadership. The point: platform safety depends on active management. If malicious actors multiply unchecked, the risk to regular users and public figures escalates. Twitter needs measurable enforcement – rate limiting, rapid takedowns, sign-in anomaly detection, stricter account creation checks, and easier reporting. Leadership can set the tone: clear accountability, transparency reports, and a dedicated emergency team for compromised verified accounts. Without that, the platform's trust erodes and scammers exploit the gap.
Two-factor confusion: Twitter Blue, 2FA and why it matters
Another angle: two-factor authentication. One tweet suggested 2FA might be limited to Twitter Blue subscribers – a serious concern if true. The author pointed out recent high-profile hacks of @dandrezner and @seungminkim, noting both were Blue accounts; it's unclear whether they had 2FA enabled. Regardless, 2FA should be available to every account and defaults should favor strong options: authenticator apps and hardware security keys, not just SMS. Twitter must clarify any feature gating that reduces safety for non-paying users. Meanwhile users should enable app-based 2FA, revoke suspicious sessions, and audit third-party apps. Platforms should also publish simple recovery steps and make 2FA settings easy to find; clear public guidance reduces panic and prevents further spread.
More from Politics
 Trends
Insurance Financial Trends: Bold Market Optimism
 Digital
Open Banking And Digital Banking Convergence: Bright Promise
 Risk
Correlation Breakdown And Portfolio Risk: Robust Outlook
 Tech